Key Statistics
Key Takeaways
- Market value: Rackmount security gateways market reached USD 202.5 million in 2026 and is projected to reach USD 526.7 million by 2036, representing a CAGR of 10.0% for 2027–2036 as customers adopt physical rack-installed enterprise firewall and security-gateway appliances integrating packet inspection, secure tunnelling and intrusion prevention across data-centre, campus and service-provider networks.
- Wired Gateways: The largest type category commands an estimated ~82% of 2026 revenue; its commercial significance arises from high-throughput protection for hybrid networks, encrypted enterprise traffic and regulated infrastructure with dependable on-premises policy enforcement. Adjacent designs compete on performance, qualification and total installed cost.
- BFSI: The leading application accounts for an estimated ~28% of 2026 sales, driven by end-user requirements for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Purchase decisions are typically channelled through enterprise network-equipment channel partners, managed service providers, security integrators and direct public-sector equipment procurement.
- North America: Leading regional expenditure accounts for an estimated ~45% of 2026 revenue, with regional growth close to ~10.1% annually. Geography reflects U.S. financial institutions, federal and regional agencies and large cloud-adjacent enterprises procure high-throughput on-premises gateways and durable maintenance support.
- Principal constraint: For rackmount security gateways, encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services govern order timing, technical acceptance and customer willingness to fund repeat production. For rackmount security gateways purchasing decisions involving regulatory cybersecurity obligations, physical demand must therefore be assessed at the level of delivered and qualified products rather than inferred from broad downstream installations.
Rackmount Security Gateways Market Overview
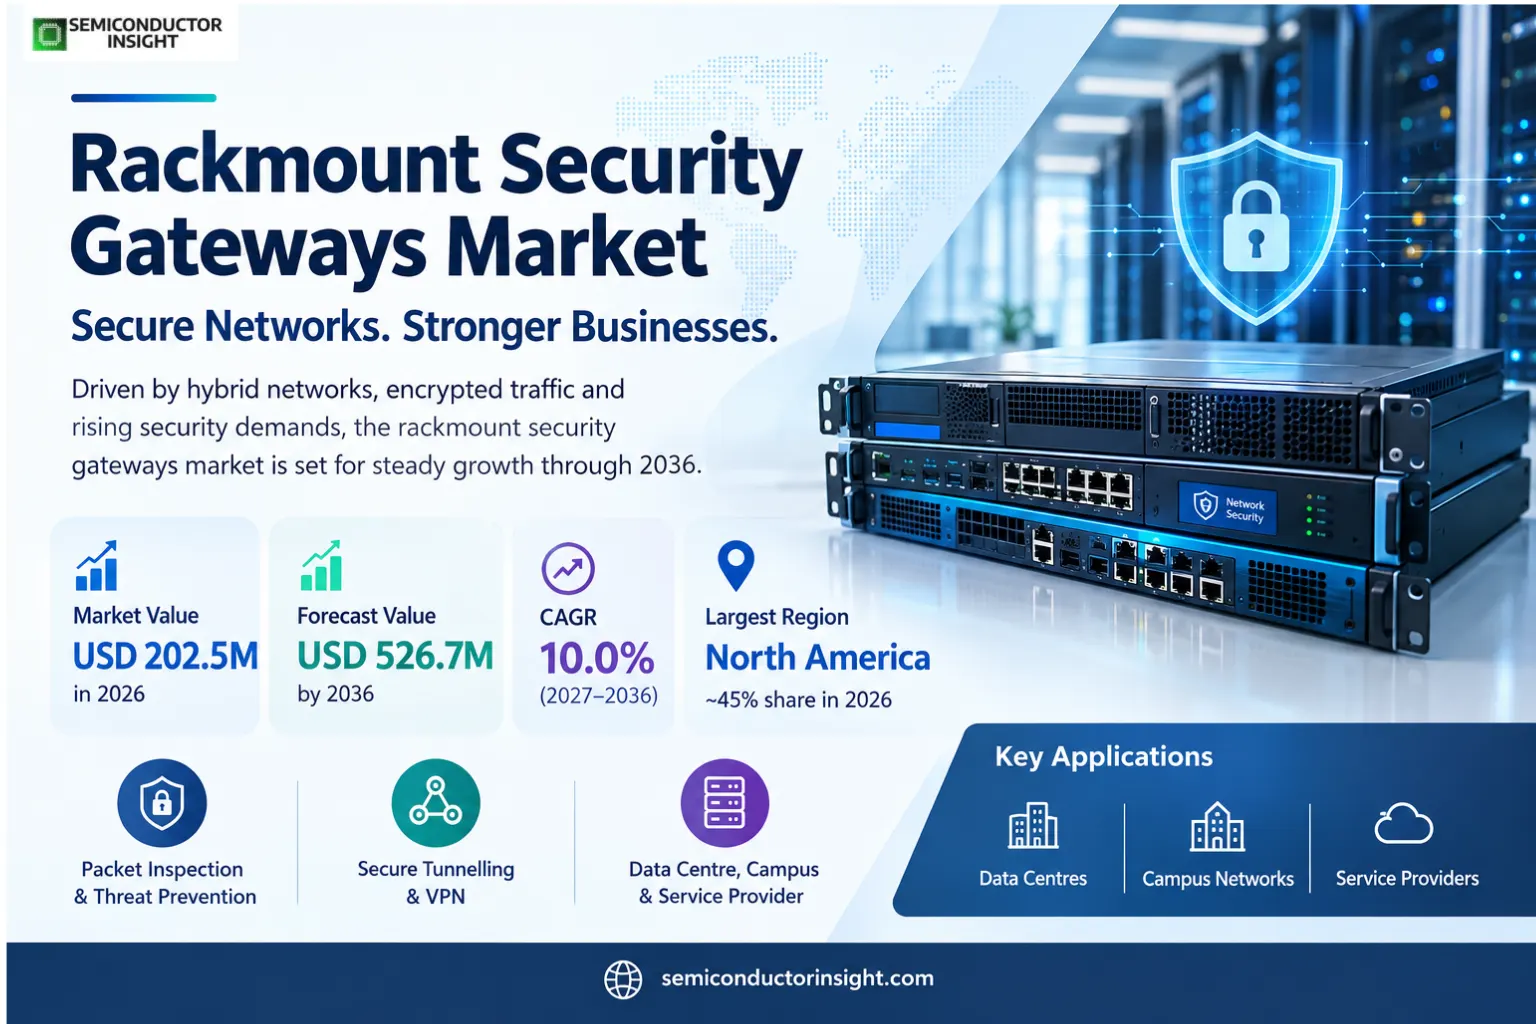
Rackmount security gateways market was valued at USD 202.5 million in 2026 and is projected to reach USD 526.7 million by 2036, at a CAGR of 10.0% during 2027–2036. North America is the largest regional market, with an estimated ~45% of 2026 expenditure. The market boundary covers standalone network-security gateway appliance hardware, not the combined platform turnover of endpoint software, cloud protection and professional services, rather than revenue from loosely connected service activities.
Rackmount security gateways market covers physical rack-installed enterprise firewall and security-gateway appliances integrating packet inspection, secure tunnelling and intrusion prevention across data-centre, campus and service-provider networks. The accounting boundary is sales of rack-mounted physical security appliances and their embedded hardware, excluding standalone cybersecurity subscriptions, cloud-delivered SASE services, endpoints and general network switching equipment.
Product scope should follow the transaction being priced: standalone network-security gateway appliance hardware, not the combined platform turnover of endpoint software, cloud protection and professional services. For that reason the analysis separates hardware purchases from wider economic activities such as rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows.
Engineering advances focus on Cisco Secure Firewall 4200 compact appliances, Palo Alto Networks PA-5400 data-centre firewalls and WatchGuard next-generation Firebox rackmounts. Equipment designers are balancing encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving managed security appliance refreshes, the most competitive solution is not necessarily the highest-throughput product: platform fit, environmental resilience and validation effort can dominate the field decision.
Demand originates in high-throughput protection for hybrid networks, encrypted enterprise traffic and regulated infrastructure with dependable on-premises policy enforcement. For rackmount security gateways purchasing decisions involving migration to cloud-native protection, as programmes move from test demonstrations to repeatable installation, operators must procure and qualify hardware at consistent volumes rather than ordering bespoke demonstration units. For rackmount security gateways purchasing decisions involving high-performance licence and service cost, this creates a larger role for standard modules, design-support documentation and distributors with verified configuration control.
The immediate market transition is toward more practical and verifiable deployments of physical rack-installed enterprise firewall and security-gateway appliances integrating packet inspection, secure tunnelling and intrusion prevention across data-centre, campus and service-provider networks. For rackmount security gateways purchasing decisions involving complex firewall policy migration, leading firms have begun to offer more integrated product families while buyers require evidence of operability under real workloads.
Segment Analysis: By Type
By type, rackmount security gateways is segmented into Wired Gateways, Wireless AC Gateways. Wired Gateways leads with an estimated ~82% of 2026 revenue and demand across enterprise IT departments, financial institutions, telecom operators, government agencies, healthcare systems and managed security service providers. For rackmount security gateways purchasing decisions involving hardware lifecycle and security vulnerabilities, the other types address alternative power, functional or mission requirements and are not interchangeable in system design.
| Type | Function | Market position |
|---|---|---|
| Wired Gateways | Wired Gateways addresses a defined performance and integration tier within rackmount security gateways. For Wired Gateways, the purchasing case depends on the customer’s target operating envelope and the integration tasks implied by predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. The Wired Gateways approval programme includes development-tool compatibility, power and thermal measurements and expected fault behaviour during normal service. | This type carries an estimated ~82% of 2026 market revenue and ~10.1% annual growth over the model window. It is the largest type and provides the reference price point. The Wired Gateways procurement category competes on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Wireless AC Gateways | Wireless AC Gateways addresses a defined performance and integration tier within rackmount security gateways. For Wireless AC Gateways, the purchasing case depends on the customer’s target operating envelope and the integration tasks implied by predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. | This type carries an estimated ~18% of 2026 market revenue and ~9.8% annual growth over the model window. It addresses a narrower deployment profile with differentiated value per unit. The Wireless AC Gateways procurement category competes on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
Secondary segmentation: By End User
By End User provides another commercial perspective on rackmount security gateways. High-throughput rackmount hardware is deployed at complex traffic and security chokepoints with central operations teams and defined service windows. The Large Enterprises class leads this particular lens, while the remaining classes serve differing runtime requirements and budgets. For rackmount security gateways purchasing decisions involving ai-assisted threat inspection appliances, commercial analysis of secondary segmentation: by end user must not add these dimensions to type-level revenue, because each is an alternative classification of the same hardware purchases.
| Axis | Members | Commercial role |
|---|---|---|
| By End User | Large Enterprises; Mid-Sized Businesses; SMBs | Large Enterprises retains the leading expenditure position within By End User. Within rackmount security gateways, this axis distinguishes engineering demand by the specification criteria of By End User and the customer purchasing role. Procurement teams review the practical distinctions among Large Enterprises, Mid-Sized Businesses, SMBs before attributing equipment revenues. By End User is another view of the same rackmount security gateways purchases; its monetary allocations are not additive to the published type totals. |
Secondary segmentation: By Security Feature
By Security Feature provides another commercial perspective on rackmount security gateways. Gateway designs differ in emphasis on deep packet inspection, intrusion signatures, application controls and managed unified threat prevention. The Firewall-Focused class leads this particular lens, while the remaining classes serve differing runtime requirements and budgets. Commercial analysis of secondary segmentation: by security feature must not add these dimensions to type-level revenue, because each is an alternative classification of the same hardware purchases.
| Axis | Members | Commercial role |
|---|---|---|
| By Security Feature | Firewall-Focused; IPS/IDS Solutions; UTM Systems | Firewall-Focused retains the leading expenditure position within By Security Feature. Within rackmount security gateways, this axis distinguishes engineering demand by the specification criteria of By Security Feature and the customer purchasing role. Procurement teams review the practical distinctions among Firewall-Focused, IPS/IDS Solutions, UTM Systems before attributing equipment revenues. By Security Feature is another view of the same rackmount security gateways purchases; its monetary allocations are not additive to the published type totals. |
Secondary segmentation: By Deployment
By Deployment provides another commercial perspective on rackmount security gateways. Datacentres prioritise multi-interface throughput and high availability while network edges and branches favour smaller form factors and simpler operations. The Data Center class leads this particular lens, while the remaining classes serve differing runtime requirements and budgets. Commercial analysis of secondary segmentation: by deployment must not add these dimensions to type-level revenue, because each is an alternative classification of the same hardware purchases.
| Axis | Members | Commercial role |
|---|---|---|
| By Deployment | Data Center; Network Edge; Branch Offices | Data Center retains the leading expenditure position within By Deployment. Within rackmount security gateways, this axis distinguishes engineering demand by the specification criteria of By Deployment and the customer purchasing role. Procurement teams review the practical distinctions among Data Center, Network Edge, Branch Offices before attributing equipment revenues. By Deployment is another view of the same rackmount security gateways purchases; its monetary allocations are not additive to the published type totals. |
Segment Analysis: By Application
By application, rackmount security gateways is divided among BFSI, Retail, IT and Telecom, Government and Public Utilities, Healthcare, Education, Others. BFSI has the largest estimated ~28% share in 2026. Customer requirements differ as strongly as enterprise IT departments, financial institutions, telecom operators, government agencies, healthcare systems and managed security service providers differ from one another.
| Application | Demand characteristics |
|---|---|
| BFSI | BFSI accounts for an estimated ~28% of 2026 market value and is modelled at roughly ~10.6% annual growth. Orders for BFSI are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Retail | Retail accounts for an estimated ~10% of 2026 market value and is modelled at roughly ~10.3% annual growth. Orders for Retail are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| IT and Telecom | IT and Telecom accounts for an estimated ~24% of 2026 market value and is modelled at roughly ~10.2% annual growth. Orders for IT and Telecom are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Government and Public Utilities | Government and Public Utilities accounts for an estimated ~18% of 2026 market value and is modelled at roughly ~9.8% annual growth. Orders for Government and Public Utilities are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Healthcare | Healthcare accounts for an estimated ~9% of 2026 market value and is modelled at roughly ~9.5% annual growth. Orders for Healthcare are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Education | Education accounts for an estimated ~6% of 2026 market value and is modelled at roughly ~9.2% annual growth. Orders for Education are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
| Others | Others accounts for an estimated ~5% of 2026 market value and is modelled at roughly ~8.9% annual growth. Orders for Others are triggered by requirements for rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows, as well as predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. |
The route to market usually passes through enterprise network-equipment channel partners, managed service providers, security integrators and direct public-sector equipment procurement. For rackmount security gateways purchasing decisions involving 5g and telecom core security, customer qualification can take longer than component or hardware production, especially where safety and interoperability are important. For rackmount security gateways purchasing decisions involving high-availability industrial network gateways, a fast-growing end market does not always translate into a similar component-revenue growth rate because replacement cycles, configuration standards and negotiated prices vary.
Regional Analysis
North America leads the global rackmount security gateways market in 2026 with an estimated ~45% share. The three largest regions are North America (~45%), Asia-Pacific (~27%), Europe (~20%), while Asia-Pacific has the fastest modelled growth at ~10.3% CAGR. Regional supply and demand are concentrated in North America through local investment and distribution networks.
How does the commercial logic differ by region in the rackmount security gateways market?
Global demand varies because encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving managed provider rackmount upgrades, north America, Europe, Asia-Pacific, South America and the Middle East and Africa therefore differ in qualification practice, operating geography and available procurement channels. For rackmount security gateways purchasing decisions involving wired gateways, local supplier support and customer experience can matter as much as technology capability when systems must be deployed and serviced at scale.
| Region | Position | Growth outlook | Demand profile | What decides supplier selection |
|---|---|---|---|---|
| Asia-Pacific | Second (~27%) | Fastest (~10.3% CAGR) | Digital-network growth and local supplier competition | Supplier selection in Asia-Pacific depends on digital-network growth and local supplier competition. China supports Huawei and domestic network-security vendors while Japan, India and South Korea deploy enterprise gateways for telecom, finance and digital public infrastructure. In Asia-Pacific, supply awards depend on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads, performance under field workloads and dependable local technical support. |
| North America | Largest (~45%) | Measured (~10.1% CAGR) | Large regulated enterprise appliance demand | Supplier selection in North America depends on large regulated enterprise appliance demand. U.S. financial institutions, federal and regional agencies and large cloud-adjacent enterprises procure high-throughput on-premises gateways and durable maintenance support. In North America, supply awards depend on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads, performance under field workloads and dependable local technical support. |
| Europe | Third (~20%) | Measured (~9.6% CAGR) | NIS2 risk management and network inspection requirements | Supplier selection in Europe depends on nis2 risk management and network inspection requirements. European regulated industries procure auditable on-premises firewalls subject to public procurement security rules and sector-specific operational resilience programmes. In Europe, supply awards depend on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads, performance under field workloads and dependable local technical support. |
| Middle East & Africa | Fourth (~5%) | Measured (~9.7% CAGR) | Transport and national digital-infrastructure security | Supplier selection in Middle East & Africa depends on transport and national digital-infrastructure security. Gulf operators procure data-centre and critical-infrastructure gateways while African telecom buyers weigh carrier security controls against procurement and maintenance budgets. In Middle East & Africa, supply awards depend on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads, performance under field workloads and dependable local technical support. |
| South America | Fifth (~3%) | Measured (~9.5% CAGR) | Regional bank and service-provider gateway refresh | Supplier selection in South America depends on regional bank and service-provider gateway refresh. Brazilian banks, telecom operators and public agencies remain major rackmount buyers; import dependence and partner support determine appliance lifecycle economics. In South America, supply awards depend on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads, performance under field workloads and dependable local technical support. |
Competitive Landscape
Competitive dynamics in rackmount security gateways span silicon or vehicle manufacturers, platform integrators and procurement intermediaries. Leading direct suppliers include Check Point, Cisco, Palo Alto Networks, Fortinet, while other profiled companies participate through adjacent platforms or customer programmes. Competition hinges on predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Product leadership is defined by real implementation experience rather than company-wide revenue. Check Point, Cisco, Palo Alto Networks, Fortinet have portfolios relevant to the sector, although each operates across a broader collection of products. For rackmount security gateways purchasing decisions involving hardware lifecycle and security vulnerabilities, it is important to assess only the relevant platform or device families when comparing supplier positions. For rackmount security gateways purchasing decisions involving ai-assisted threat inspection appliances, procurement wins also depend on reference designs, channel access and capability to fix deployment issues after installation.
Suppliers compete across multiple qualification thresholds. Buyers seek predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads and increasingly request integration toolchains, compliance records and known configurations. For rackmount security gateways purchasing decisions involving 5g and telecom core security, continuous product revisions must be compatible with the customer’s service life and existing assets. For rackmount security gateways purchasing decisions involving high-availability industrial network gateways, as a result, early price discounts do not guarantee a design win unless a supplier can maintain support through complete deployment cycles.
Adjacent companies are influential without necessarily supplying the market-defining device. Managed security service providers, Enterprise IT security teams, Government network operators can affect platform specifications, distribution or adoption economics, while other manufacturers supply supporting electronics. For rackmount security gateways purchasing decisions involving managed provider rackmount upgrades, including the entire revenue of a service platform or parent company would overstate the equipment market.
For rackmount security gateways purchasing decisions involving wired gateways, the most durable commercial advantage comes from repeatable delivery rather than isolated demonstrations. For rackmount security gateways purchasing decisions involving wireless ac gateways, component traceability, repair logistics, manufacturing capacity and the ability to meet an OEM testing protocol are material competitive factors. When encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services, customers favour suppliers capable of maintaining stable product revisions.
Tier structure
| Tier | Companies | Basis of competition |
|---|---|---|
| Tier 1 | Check Point, Cisco, Palo Alto Networks, Fortinet | For rackmount security gateways purchasing decisions involving bfsi, direct hardware suppliers compete on a combination of validated product capability and timely deliveries. The relevant offering must satisfy predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. For rackmount security gateways purchasing decisions involving retail, when evaluating the Tier 1 category, purchasers consider interoperability, component life and testing evidence, not simply the supplier’s brand. |
| Tier 2 | SonicWall, WatchGuard, Sophos, Barracuda Networks | Specialised vendors concentrate on narrower functional or customer niches. Their products may offer favourable trade-offs against encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving it and telecom, for the Tier 2 supplier group, sales opportunities depend on the buyer’s willingness to support additional integration and qualification work. |
| Ecosystem | Managed security service providers, Enterprise IT security teams, Government network operators | For rackmount security gateways purchasing decisions involving government and public utilities, systems and service participants influence the final design without always producing the market-defining hardware. The Ecosystem participants shape customer requirements, installation plans and acceptance criteria connected to rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows. For rackmount security gateways purchasing decisions involving healthcare, including the full revenue of these Ecosystem participants as direct product-market sales would double-count adjacent activity. |
Key companies profiled
- Check Point Software Technologies
- Cisco Systems
- Palo Alto Networks
- Fortinet
- Dell SonicWALL
- Juniper Networks
- Huawei Technologies
- DPtech
- Ruijie Networks
- Barracuda Networks
- Sangfor Technologies
- WatchGuard Technologies
- Sophos
- Hillstone Networks
- IT Central Station
Production Capacity Analysis
Production in the rackmount security gateways market combines product development, contracted manufacture, test and field qualification. Capacity must be evaluated for the equipment covered by sales of rack-mounted physical security appliances and their embedded hardware, excluding standalone cybersecurity subscriptions, cloud-delivered SASE services, endpoints and general network switching equipment. For rackmount security gateways purchasing decisions involving education, supplier output depends on reliable upstream components and the availability of teams able to certify each platform generation.
Upstream manufacturing begins with specialised equipment and electronics matched to physical rack-installed enterprise firewall and security-gateway appliances integrating packet inspection, secure tunnelling and intrusion prevention across data-centre, campus and service-provider networks. For rackmount security gateways purchasing decisions involving others, designs are converted into repeatable builds using supplier-qualified parts, automated verification and controlled firmware releases. For rackmount security gateways purchasing decisions involving encrypted enterprise traffic growth, factories operating multiple programmes must schedule production batches according to expected customer acceptance and servicing demand.
Diversified production and overseas service centres have a direct effect on the cost of rackmount security gateways. For rackmount security gateways purchasing decisions involving regulatory cybersecurity obligations, for customers operating across continents, replacement units and regulatory documentation can be as important as local final assembly. For rackmount security gateways purchasing decisions involving secure data-center network segmentation, companies may therefore dual-source electronics or maintain additional field-stock hubs where import lead times are unpredictable.
The practical bottlenecks include encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving managed security appliance refreshes, manufacturers must control incoming components, update software securely and demonstrate consistent performance in representative operating conditions. For rackmount security gateways purchasing decisions involving migration to cloud-native protection, a design sold into a regulated mission cannot be readily modified without further validation.
Market Dynamics
Market dynamics reflect customer demand for high-throughput protection for hybrid networks, encrypted enterprise traffic and regulated infrastructure with dependable on-premises policy enforcement, balanced against encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving high-performance licence and service cost, the drivers below describe directional factors on growth rather than independently measured contributions to the headline forecast.
MARKET DRIVERS
Drivers Impact Analysis*
| Driver | (~) % impact on CAGR forecast | Geographic relevance | Impact timeline |
|---|---|---|---|
| Encrypted enterprise traffic growth | +0.3% | Global / selected adopter markets | 2026–2036 |
| Regulatory cybersecurity obligations | +0.5% | Global / selected adopter markets | 2026–2036 |
| Secure data-center network segmentation | +0.6% | Global / selected adopter markets | 2026–2036 |
| Managed security appliance refreshes | +0.8% | Global / selected adopter markets | 2026–2036 |
| Fleet or installed-base renewal | +0.9% | Global / selected adopter markets | 2026–2036 |
Encrypted enterprise traffic growth
Encrypted enterprise traffic growth supports demand for rackmount security gateways. The commercial effect of encrypted enterprise traffic growth is observed when customers require rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows in a reliable operating environment. Purchasers affected by encrypted enterprise traffic growth translate requirements into specifications for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Regulatory cybersecurity obligations
Regulatory cybersecurity obligations supports demand for rackmount security gateways. The commercial effect of regulatory cybersecurity obligations is observed when customers require rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows in a reliable operating environment. Purchasers affected by regulatory cybersecurity obligations translate requirements into specifications for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Secure data-center network segmentation
Secure data-center network segmentation supports demand for rackmount security gateways. The commercial effect of secure data-center network segmentation is observed when customers require rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows in a reliable operating environment. Purchasers affected by secure data-center network segmentation translate requirements into specifications for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Managed security appliance refreshes
Managed security appliance refreshes supports demand for rackmount security gateways. The commercial effect of managed security appliance refreshes is observed when customers require rack-mounted firewall installations, gateway policies enforced and protected east-west or internet-bound traffic flows in a reliable operating environment. Purchasers affected by managed security appliance refreshes translate requirements into specifications for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
MARKET RESTRAINTS
Restraints Impact Analysis*
| Restraint | (~) % impact on CAGR forecast | Geographic relevance | Impact timeline |
|---|---|---|---|
| Migration to cloud-native protection | -0.2% | Selected end markets | 2026–2036 |
| High-performance licence and service cost | -0.3% | Selected end markets | 2026–2036 |
| Complex firewall policy migration | -0.4% | Selected end markets | 2026–2036 |
| Hardware lifecycle and security vulnerabilities | -0.6% | Selected end markets | 2026–2036 |
Migration to cloud-native protection
Migration to cloud-native protection can delay expenditure on rackmount security gateways. Buyers facing encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services may reduce fleet growth, defer system integration or select lower-cost equipment with longer lead times. The response to migration to cloud-native protection requires suppliers to prove performance and offer maintainable lifecycle commitments to overcome these constraints.
High-performance licence and service cost
High-performance licence and service cost can delay expenditure on rackmount security gateways. In service networks supporting High-performance licence and service cost, buyers facing encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services may reduce fleet growth, defer system integration or select lower-cost equipment with longer lead times.
Complex firewall policy migration
Complex firewall policy migration can delay expenditure on rackmount security gateways. When selecting equipment for Complex firewall policy migration, buyers facing encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services may reduce fleet growth, defer system integration or select lower-cost equipment with longer lead times.
Hardware lifecycle and security vulnerabilities
Hardware lifecycle and security vulnerabilities can delay expenditure on rackmount security gateways. Across supply agreements concerning Hardware lifecycle and security vulnerabilities, buyers facing encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services may reduce fleet growth, defer system integration or select lower-cost equipment with longer lead times.
MARKET OPPORTUNITIES
AI-assisted threat inspection appliances
AI-assisted threat inspection appliances provides a route into adjacent customer segments for rackmount security gateways. The commercial opportunity is to solve a specific deployment problem involving predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. New offerings targeting ai-assisted threat inspection appliances need documented interoperability, reliable suppliers and credible post-sale support.
5G and telecom core security
5G and telecom core security provides a route into adjacent customer segments for rackmount security gateways. For customers assessing 5G and telecom core security, the commercial opportunity is to solve a specific deployment problem involving predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
High-availability industrial network gateways
High-availability industrial network gateways provides a route into adjacent customer segments for rackmount security gateways. In procurement programmes centred on High-availability industrial network gateways, the commercial opportunity is to solve a specific deployment problem involving predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Managed provider rackmount upgrades
Managed provider rackmount upgrades provides a route into adjacent customer segments for rackmount security gateways. Within field deployments associated with Managed provider rackmount upgrades, the commercial opportunity is to solve a specific deployment problem involving predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads.
Supply Chain Analysis
The value chain for rackmount security gateways links design and qualification to production, distribution and field support. Its revenue boundary remains standalone network-security gateway appliance hardware, not the combined platform turnover of endpoint software, cloud protection and professional services. Product sourcing is complicated by encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services.
Upstream. The upstream stage influences cost and reliability for rackmount security gateways. Upstream participants manage encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services while protecting availability of parts and validated software. For rackmount security gateways purchasing decisions involving complex firewall policy migration, work at the upstream stage must support traceable revisions, acceptance documentation and the customer’s maintenance model.
Manufacturing. The manufacturing stage influences cost and reliability for rackmount security gateways. Manufacturing participants manage encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services while protecting availability of parts and validated software. For rackmount security gateways purchasing decisions involving hardware lifecycle and security vulnerabilities, work at the manufacturing stage must support traceable revisions, acceptance documentation and the customer’s maintenance model.
Channel. The channel stage influences cost and reliability for rackmount security gateways. Channel participants manage encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services while protecting availability of parts and validated software. For rackmount security gateways purchasing decisions involving ai-assisted threat inspection appliances, work at the channel stage must support traceable revisions, acceptance documentation and the customer’s maintenance model.
Downstream. The downstream stage influences cost and reliability for rackmount security gateways. Downstream participants manage encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services while protecting availability of parts and validated software. For rackmount security gateways purchasing decisions involving 5g and telecom core security, work at the downstream stage must support traceable revisions, acceptance documentation and the customer’s maintenance model.
Recent Developments
- 22 September 2026 Announced
ENISA reported enisa threat landscape 2026 on 22 September 2026. For rackmount security gateways purchasing decisions involving high-availability industrial network gateways, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. For rackmount security gateways customers, the significance is the relationship between enisa threat landscape 2026 and the choice of predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Source - 29 June 2026 Announced
WatchGuard reported firebox m290 retirement and m295 replacement on 29 June 2026. From the perspective of operators using 29 June 2026 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. Source - 29 May 2026 Announced
WatchGuard reported high-performance firebox m4850 / m5850 / m6850 availability on 29 May 2026. In lifecycle planning for 29 May 2026 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. Source - 14 May 2026 Announced
WatchGuard reported firebox m590 and m690 end of sale on 14 May 2026. In service networks supporting 14 May 2026 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. For rackmount security gateways customers, the significance is the relationship between firebox m590 and m690 end of sale and the choice of predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Source - 27 February 2026 Announced
Palo Alto Networks reported pa-5400 next generation firewall datasheet on 27 February 2026. For customers assessing 27 February 2026 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. For rackmount security gateways customers, the significance is the relationship between pa-5400 next generation firewall datasheet and the choice of predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Source - 7 October 2025 Announced
WatchGuard reported firebox m series rackmount launch on 7 October 2025. From the perspective of operators using 7 October 2025 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. For rackmount security gateways customers, the significance is the relationship between firebox m series rackmount launch and the choice of predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Source - 1 October 2025 Announced
ENISA reported enisa threat landscape 2025 on 1 October 2025. In lifecycle planning for 1 October 2025 Announced release, the first-party statement identifies a concrete product line, commercial release or platform partnership, allowing procurement teams to inspect the named capability instead of relying on broad technology claims. For rackmount security gateways customers, the significance is the relationship between enisa threat landscape 2025 and the choice of predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Source
REPORT SCOPE & SEGMENTATION
| Attribute | Details |
|---|---|
| Study Period | 2021–2036 |
| Historical Period | 2021–2025 |
| Base Year | 2026 |
| Estimated Year | 2027 |
| Forecast Period | 2027–2036 |
| 2026 Market Size | USD 202.5 million |
| 2027 Estimated Size | USD 222.8 million |
| 2036 Forecast Size | USD 526.7 million |
| CAGR (2027–2036) | 10.0% |
| Unit | USD million; product-level supplier revenue |
| Market Definition | sales of rack-mounted physical security appliances and their embedded hardware, excluding standalone cybersecurity subscriptions, cloud-delivered SASE services, endpoints and general network switching equipment |
| By Type | Wired Gateways · Wireless AC Gateways |
| By Application | BFSI · Retail · IT and Telecom · Government and Public Utilities · Healthcare · Education · Others |
| By End User | Large Enterprises · Mid-Sized Businesses · SMBs |
| By Security Feature | Firewall-Focused · IPS/IDS Solutions · UTM Systems |
| By Deployment | Data Center · Network Edge · Branch Offices |
| By Region | For rackmount security gateways purchasing decisions involving managed provider rackmount upgrades, regional revenue values are attributed to the procurement geography; the estimate includes five global regions. Asia-PacificChina, Japan, South Korea, India North AmericaUnited States, Canada, Mexico EuropeGermany, France, United Kingdom, Italy Middle East & AfricaSaudi Arabia, United Arab Emirates, South Africa South AmericaBrazil, Argentina, Chile |
| Key Companies Profiled | Check Point Software Technologies, Cisco Systems, Palo Alto Networks, Fortinet, Dell SonicWALL, Juniper Networks, Huawei Technologies, DPtech, Ruijie Networks, Barracuda Networks, Sangfor Technologies, WatchGuard Technologies, Sophos, Hillstone Networks, IT Central Station |
| Customization Scope | Country-level type and application revenue, manufacturer capability, buying-channel mapping, technical qualification, systems design and pricing for rackmount security gateways. |
Frequently Asked Questions
What is the size and forecast of the rackmount security gateways market?
The market is valued at USD 202.5 million in 2026 and is projected to reach USD 526.7 million by 2036, representing CAGR of 10.0% over 2027–2036. The category covers physical rack-installed enterprise firewall and security-gateway appliances integrating packet inspection, secure tunnelling and intrusion prevention across data-centre, campus and service-provider networks. For rackmount security gateways purchasing decisions involving wired gateways, buyers should compare these figures only with similarly bounded product revenue rather than service or system totals from adjacent categories.
Which type has the largest share in the rackmount security gateways market?
Wired Gateways is the largest type with an estimated ~82% share of 2026 value. It is supported by high-throughput protection for hybrid networks, encrypted enterprise traffic and regulated infrastructure with dependable on-premises policy enforcement. For rackmount security gateways purchasing decisions involving wireless ac gateways, the remaining categories meet different operating envelopes, so an equipment producer may need multiple solutions even when the leading class captures most of the market revenue.
Which application leads rackmount security gateways demand?
BFSI leads with an estimated ~28% of 2026 revenue. This application values predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. For rackmount security gateways purchasing decisions involving bfsi, demand is converted into sales when customers pass their engineering and acceptance tests, establish operating procedures and secure a source of spare devices or replacement equipment.
Which is the largest regional market for rackmount security gateways?
North America leads with an estimated ~45% of 2026 revenue, while Asia-Pacific has the quickest modeled expansion. In service networks supporting FAQ: Which is the largest regional market for rackmount security gateways?, u.S. financial institutions, federal and regional agencies and large cloud-adjacent enterprises procure high-throughput on-premises gateways and durable maintenance support.
What drives growth in the rackmount security gateways market?
The strongest underlying driver is high-throughput protection for hybrid networks, encrypted enterprise traffic and regulated infrastructure with dependable on-premises policy enforcement. Equipment must still meet customer requirements for predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. For rackmount security gateways purchasing decisions involving retail, suppliers that can combine reliable performance with software and integration support are better positioned to convert demonstrations into repeatable procurement programmes.
What limits wider adoption of rackmount security gateways?
Important restrictions include encrypted traffic inspection overhead, product lifecycle replacement, subscription bundling, heterogeneous security policy management and migration of some perimeter controls into cloud services. For rackmount security gateways purchasing decisions involving it and telecom, these concerns affect schedules and the proportion of potential users ready to fund deployments. For rackmount security gateways purchasing decisions involving government and public utilities, vendors can mitigate part of the risk with documented validation, long-term maintenance agreements and multiple qualified sources, but they cannot remove all policy or operating constraints.
Which companies are profiled in the rackmount security gateways market?
The company coverage includes Check Point Software Technologies, Cisco Systems, Palo Alto Networks, Fortinet, Dell SonicWALL, Juniper Networks. For rackmount security gateways purchasing decisions involving healthcare, some names are directly relevant equipment suppliers while others participate through adjacent technologies, platform procurement or integration partnerships. For rackmount security gateways purchasing decisions involving education, commercial assessment should distinguish direct product revenue from other corporate sales to avoid false market-share comparisons.
How is rackmount security gateways segmented?
Type segments comprise Wired Gateways, Wireless AC Gateways. Application categories comprise BFSI, Retail, IT and Telecom, Government and Public Utilities, Healthcare, Education, Others. For rackmount security gateways purchasing decisions involving others, these dimensions describe the same global expenditure from different perspectives and should not be added together. For rackmount security gateways purchasing decisions involving encrypted enterprise traffic growth, geographic coverage spans North America, Europe, Asia-Pacific, South America and Middle East and Africa.
How does innovation affect supplier choice in the rackmount security gateways market?
Innovations centre on Cisco Secure Firewall 4200 compact appliances, Palo Alto Networks PA-5400 data-centre firewalls and WatchGuard next-generation Firebox rackmounts. Their commercial value depends on how effectively the customer can deploy them, including predictable inspected throughput, resilient high-availability deployment, secure VPN termination and manageable firewall policy under real encrypted workloads. Companies increasingly choose products with clear technical support, mature software or mission controls and predictable maintenance instead of paying solely for maximum specifications.
What does the rackmount security gateways study include and exclude?
The scope includes sales of rack-mounted physical security appliances and their embedded hardware, excluding standalone cybersecurity subscriptions, cloud-delivered SASE services, endpoints and general network switching equipment. For rackmount security gateways purchasing decisions involving regulatory cybersecurity obligations, it excludes unrelated revenues from surrounding services and infrastructure so that segment and regional comparisons remain meaningful. For rackmount security gateways purchasing decisions involving secure data-center network segmentation, the analysis covers production capability, competitive positioning, procurement practices, growth forces and leading product categories in a 2026 base-year and 2036 forecast framework.
Research Sources & Evidence Base
Get Sample Report PDF for Exclusive Insights
Report Sample Includes
- Table of Contents
- List of Tables & Figures
- Charts, Research Methodology, and more...
 Download Sample Report PDF