Key Statistics
Key Takeaways
- Market trajectory: Embedded protection integrated into electronic equipment is projected to expand from USD 8,200 million in 2025 to USD 15,600 million by 2034. The implied 7.4% annual increase reflects a broader collection of hardware-rooted, software-led and combined designs, including secure launch and device-update capabilities.
- Solution architecture: Hardware-rooted offerings lead with an estimated ~56% of market value; software-focused approaches hold an estimated ~27% and hybrid designs an estimated ~17%. Product decisions turn on the isolation needed for firmware integrity, the capacity of host silicon and whether the supplier can maintain deployed code.
- Application mix: Industrial IoT is the leading application at an estimated ~29%, with automotive deployments at an estimated ~27%. Protected control software reduces the opportunity for unauthorized changes to systems that monitor physical processes, while connected vehicle electronics create demanding authentication and update use cases.
- Regional market: Asia-Pacific represents an estimated ~37% of the market, ahead of North America at an estimated ~28% and Europe at an estimated ~26%. These positions reflect embedded product manufacturing, software engineering, automotive demand and supply of security-capable processors, with substantial cross-border integration.
- Security priorities: Secure boot commands an estimated ~37% of functional demand, while authenticated over-the-air updates contribute an estimated ~27%. Suppliers need to show not only how a device initially trusts its code, but also how it can recover safely when software must be replaced years later.
Embedded Security Market Overview
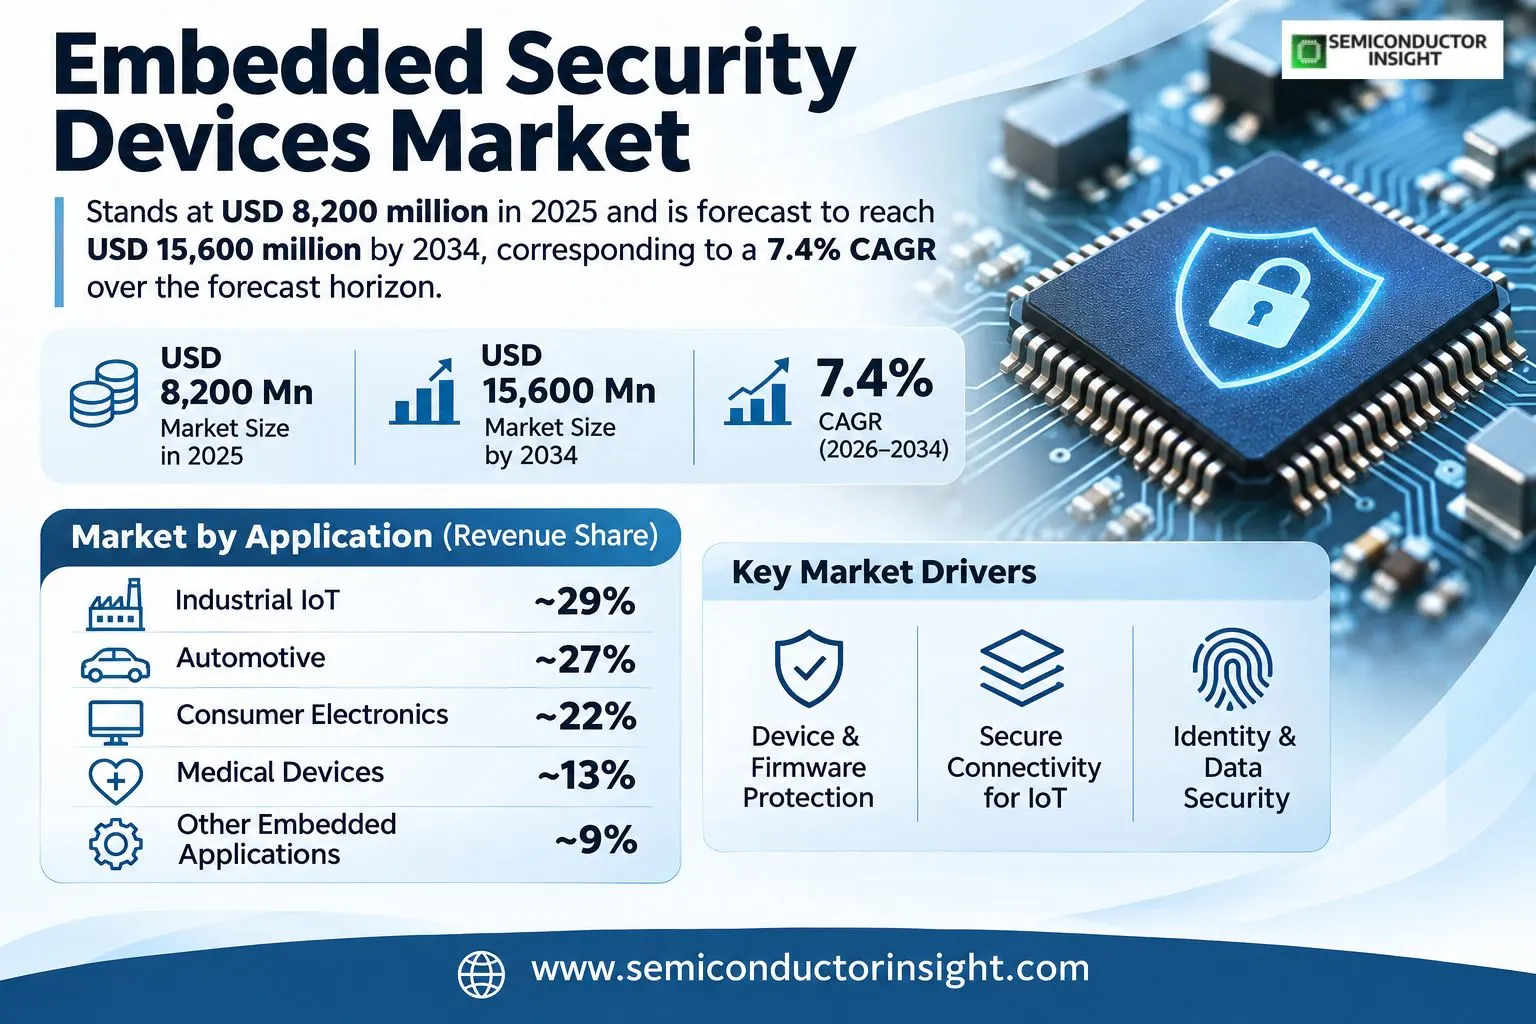
Embedded security market stands at USD 8,200 million in 2025 and is forecast to reach USD 15,600 million by 2034, corresponding to a 7.4% CAGR over the forecast horizon. Security controls built into controllers and the firmware surrounding them protect increasingly connected products against unauthorized code, unsafe modifications and compromised identities.
Embedded security combines silicon protection mechanisms with privileged code, trusted execution environments and ongoing software safeguards applied inside an electronic device. Typical functions include verifying firmware at startup, separating sensitive operations from ordinary applications, authenticating installed components and rejecting unauthorized remote updates. These capabilities are relevant to microcontrollers in vehicles, factories, medical equipment and connected consumer devices, where a conventional network firewall cannot directly protect every local physical controller.
A system begins with a trust decision about which firmware may run. A fixed or protected first boot stage checks a signature or digest, after which later software layers can be accepted only through a defined chain. Isolated execution, secure key custody and protected debugging may provide further separation. Update protection is especially important for products that remain in operation after a vulnerability is identified or after a third-party service changes its requirements.
The revenue boundary includes trusted processor features, embedded security software, firmware security frameworks, protected update functionality and combined security offerings sold as part of the defined device-level system. It also includes embedded services directly belonging to security lifecycle operation when covered by the product offering. Stand-alone corporate firewalls, unrelated cloud monitoring subscriptions, whole-device selling prices and independent cybersecurity consulting fall outside this market.
Security architecture must match the economic and operational constraints of the host device. An industrial controller may require deterministic execution and service availability, while an electronic control unit in a vehicle needs predictable update management and long qualification cycles. Connected healthcare equipment raises questions about patient safety and access to secure maintenance. The size and sophistication of the trust environment can therefore vary without changing the fundamental need to verify what code and credentials a device is allowed to use.
Segment Analysis: By Type
Hardware-rooted security captures an estimated ~56% of the type mix, while software-based security represents an estimated ~27% and combined hardware/software solutions an estimated ~17%. The three categories describe how a protection system is built and maintained, not mutually exclusive threats. A single electronic product can use hardware isolation alongside update signing and runtime integrity software.
| Type | Function | Market position |
|---|---|---|
| Hardware-Rooted Security | Largest type, an estimated ~56%. Trust anchors embedded in a microcontroller or processor hold protected secrets and verify selected stages of software execution. STMicroelectronics documents multiple secure boot paths in the STM32H5 family, showing that capabilities vary even within one controller generation. The STM32H503 has no TrustZone support, while STM32H523, STM32H543, STM32H563 and STM32H5Ex variants support forms of protected isolation. Security-oriented STM32H533, STM32H553, STM32H573 and STM32H5F5 devices offer additional hardware cryptographic options in specified configurations. The secure boot mechanism can use an STiRoT initial immutable root, an OEMiRoT alternative and an OEMuRoT updatable stage depending on the chosen device. The presence of processor hardware does not eliminate the need for OEM threat analysis and an appropriate secure provisioning process. The supplier also identifies different STM32H5 hardware-protected regions and lifecycle policies, requiring review of reference manuals and product-specific option bytes. The STM32H5 reference materials distinguish the STM32H503, STM32H523, STM32H533, STM32H543, STM32H553, STM32H563, STM32H573 and STM32H5F5 product lines for different hardware security services. ST also groups certain characteristics by STM32H5Ex, STM32H56x and STM32H57x variants. For the STM32H503, the absence of Arm TrustZone changes software isolation design; STM32H523 and STM32H543 families expose other options, while STM32H533, STM32H553 and STM32H573 support enhanced cryptographic startup in selected configurations. A protected STM32H573 design can use an initial immutable stage before a second updatable root, giving equipment engineers at least 2 boot-stage responsibilities to test. ST identifies protected boot memory starting near address 0x0C000000 in its technical guidance, but memory map decisions remain specific to the exact STM32 controller. Runtime isolation can involve Armv8-M Secure and Nonsecure states and target PSA isolation level 3 on supported platforms. The ST Secure Manager feature descriptions refer to PSA certification level 3 and GlobalPlatform SESIP 3 targets, which are assurance objectives to verify on the actual device and software combination. On selected STM32H5Fx or STM32H573 parts, a secure manager may expose initial attestation alongside code-signing services; the STM32H56x line does not provide the same supported feature set. Debug authentication and HDP controls may complement a 2-stage boot path with a level 2 or level 3 memory protection phase. These chip identifiers and assurance levels describe distinctions among available implementation paths, not product shipment or revenue statistics. Different design families provide different access to AES encryption accelerators, public-key verification, protected flash regions and runtime isolation, so the equipment manufacturer must validate its actual selected part. | Hardware protection may be selected early during board design, but the resulting trust anchor affects software integration throughout product support. An estimated ~56% share reflects demand in safety-conscious and industrial environments where protected boot paths and controlled key handling are difficult to replace with ordinary application code. Certification needs depend on the final system boundary rather than a generic security label. |
| Software-Based Security | Configurable protection, an estimated ~27%. Embedded software establishes policies for verifying binaries, checking device configurations and handling encrypted updates. Firmware running within a trusted execution environment can protect cryptographic material and restrict access by nonsecure applications, provided the processor implements the needed isolation. ST Secure Manager on supported STM32H5 devices presents secure boot, crypto services, initial attestation, secure storage and firmware update interfaces under Arm Platform Security Architecture concepts. Development may use STM32Cube tools and selected ST-provided libraries to compose the secure and nonsecure sides of an application. Software protection is flexible, but it cannot withstand every physical attack if the underlying hardware lacks an appropriate trust boundary. ST software engineering tools illustrate the significance of revision matching. One supported setup refers to STM32H573 hardware on the MB1677 development board and the X-CUBE-SEC-M-H5_V2.1.0 package. The associated STM32CubeProgrammer recommendation is version V2.19.0 or later. The STM32H57 environment differs from the STM32H56, STM32H523 and STM32H503 paths, so the same secure manager binary does not serve every STM32H5 MCU. A project may use a 2-level root with 1 immutable stage and 1 updatable stage. Its secure and nonsecure worlds require compatible source and linker configuration, and the chosen STM32Cube firmware release must match that arrangement. At the developer level, reference documents RM3254, RM0481, UM2237, UM2238, AN5054, AN2606 and AN4992 cover different registers, product behavior, programming and system memory choices. An STM32H573 engineer should check RM3254 against RM0481 when investigating version-specific security guidance rather than equate their roles. Secure Manager resources also name X-CUBE-SEC-M-H5 and access kits supporting nonsecure development. Keeping a tested combination of tool versions and board options is often more consequential than a single advertised cryptographic benchmark. | Software lifecycle economics differ from those of discrete chips: the same security framework may need regular integration testing, vulnerability updates and developer support across changing application versions. Manufacturers consider tools, long-term compatibility and code-signing operations before standardizing a platform. A supplier with dependable reference implementations may reduce engineering cost while still leaving responsibility for final product validation with the OEM. |
| Hybrid Solutions | Combined security programs, an estimated ~17%. Hybrid designs unite a protected boot anchor with securely maintained firmware and operational services. A device may rely on an isolated root key, software policy checks at runtime and a cloud distribution system that delivers authenticated packages. Critical decisions concern recovery after a failed update, response when a key is compromised and the separation between application administrators and trust administrators. Engineers must also prevent update mechanisms from becoming a route for unauthorized code, especially where wireless connectivity and unattended operation make manual inspection impractical. | Hybrid deployments fit products whose threat exposure evolves after delivery. An automotive controller may receive software fixes through a managed distribution chain, while an industrial sensor may verify new firmware without exposing its calibration data. Suppliers compete on a complete workflow from initial enrollment to decommissioning rather than simply offering more cryptographic algorithm names. |
Secondary segmentation: buyers and protection tasks
Embedded security purchasing can be grouped by who integrates it, which function receives the greatest investment and what sector owns the deployed device. Automotive engineers may favor controlled boot and update authorization; hospital equipment developers pay close attention to service access and availability. Original equipment manufacturers usually define the trust architecture before contracting the software and semiconductor subsystems needed to implement it.
| Axis | Members | Commercial role |
|---|---|---|
| End User | OEMs; System Integrators; Device Manufacturers | Product owners, application integrators and assembly businesses contribute different stages of security deployment. |
| Security Function | Secure Boot; Runtime Attestation; Over-the-Air (OTA) Update Protection; Key Management | Start-up code verification, running state evidence, software distribution and credential custody have distinct roles. |
| Industry Vertical | Automotive & Transportation; Healthcare & Medical; Energy & Utilities; Smart Home & Consumer | Long-life safety systems and high-volume connected goods impose varied qualification and patching requirements. |
Segment Analysis: By Application
Industrial IoT leads application spending at an estimated ~29%, followed by automotive at an estimated ~27%, consumer electronics at an estimated ~22%, medical devices at an estimated ~13% and other embedded applications at an estimated ~9%. Protection is generally specified where a compromised controller could threaten equipment reliability, trusted data or safety.
| Application | Demand characteristics |
|---|---|
| Industrial IoT | Leading application, an estimated ~29%. Industrial machines increasingly exchange diagnostic data, production instructions and firmware updates through plant networks. An attacker who alters local controller software may affect physical processes rather than only steal ordinary digital records. Embedded security can bind the system to an approved software image and restrict maintenance access. It must also work with deterministic control loops and established equipment lifecycles. System suppliers therefore consider secure boot integration alongside patch windows and recovery procedures. |
| Automotive | Large application, an estimated ~27%. Vehicle electronic control units, gateways and sensor processors share communications pathways while controlling many distinct functions. Security engineering has to address signed firmware, diagnostic access, authorized updates and protected credential handling across supplier relationships. Product roadmaps are shaped by OEM qualification and software release management. Vehicle safety and cybersecurity are interconnected concerns, but secure code signing alone does not demonstrate full system safety compliance. |
| Consumer Electronics | Broad unit demand, an estimated ~22%. Connected cameras, smart-home hubs, personal devices and entertainment equipment need a defensible path for updates and identity verification. Resource-constrained hardware may employ compact trust features built into the main controller. Customers may seldom inspect the implementation directly, but product brands carry responsibility for responding to exploitable vulnerabilities over an agreed support period. Design teams consequently evaluate developer tools and upgrade reliability. |
| Medical Devices | Safety-linked controls, an estimated ~13%. Connected diagnostic and therapeutic equipment requires careful handling of software changes and authorization to service interfaces. Unauthorized updates could degrade equipment behavior or expose sensitive data. Manufacturers may combine digitally signed software with protected processor regions and strict clinical servicing processes. Engineering teams need to balance cyberattack resistance against safe fallback behavior and the possibility of limited network availability at a care site. |
| Others | Additional embedded domains, an estimated ~9%. Energy distribution instrumentation, retail equipment, connected transportation infrastructure and specialty sensing systems employ a wide variety of embedded controllers. The security objective may be to reject counterfeit hardware, restrict firmware modification or protect a remote maintenance command. Application-specific engineering is decisive because a remote field device may have little memory and no direct operator interface when a security incident occurs. |
Purchasers increasingly ask security suppliers for evidence that protection remains operational after installation. An application architecture should specify who authorizes firmware releases, how updates are authenticated and whether an older vulnerable version can be reinstalled. Maintaining visibility into a fleet of deployed devices is often an essential extension of embedded software integrity rather than a separate one-time hardware specification.
Regional Analysis
Asia-Pacific is the largest regional market with an estimated ~37% share, reflecting its extensive manufacture of connected electronics and security-capable processors. North America follows at an estimated ~28%, Europe represents an estimated ~26%, and South America and Middle East & Africa account for approximately ~5% and ~4% respectively. Embedded software engineering and local product standards make each region distinct.
Where are integrated device-protection architectures being deployed?
Demand does not originate at a single moment in a security product supply chain. A processor can be architected in one region, its secure firmware developed in another and the finished device installed somewhere else. The geographic picture therefore combines engineering investment, assembly capacity, infrastructure upgrades and the lifecycle obligations of equipment owners. A stronger regional presence may indicate large-scale device production rather than direct local expenditure on independent security software.
| Region | Position | Growth outlook | Demand profile | What decides supplier selection |
|---|---|---|---|---|
| Asia-Pacific | Largest (~37%) | Fast (~8.0% CAGR) | Connected electronics and industrial controls | Hardware and firmware platform integration |
| North America | Second (~28%) | Strong (~7.1% CAGR) | Security architecture and cloud connectivity | Security software lifecycle |
| Europe | Third (~26%) | Strong (~7.0% CAGR) | Vehicle engineering and regulatory focus | Long-lifecycle certified design |
| South America | Growing (~5%) | Selective (~6.9% CAGR) | Payments and industrial automation | Field upgrade management |
| Middle East & Africa | Growing (~4%) | Selective (~7.6% CAGR) | Energy, telecom and infrastructure | Remote trust operations |
Key Embedded Security Manufacturers and Competitive Landscape
Major competitors supply security-capable controllers, processor IP, trusted firmware and supporting development environments. NXP Semiconductors, Infineon Technologies, Renesas Electronics, Microchip Technology, STMicroelectronics, Texas Instruments, Qualcomm, Samsung Electronics, Broadcom, Analog Devices and Marvell compete across different embedded platforms. The buyer selects an ecosystem capable of maintaining device integrity over a product lifetime, not merely a supplier offering a cryptographic engine.
STMicroelectronics provides secure firmware architecture for selected STM32 platforms, including a Secure Manager environment that exposes PSA-aligned security services. NXP combines hardware roots of trust with host software libraries, and Microchip supports cryptographic authentication and secure startup in connected controller applications. Renesas and Texas Instruments address embedded computing and industrial design needs through their respective controller ecosystems. Because software capabilities differ by chip series and configuration, the existence of a security feature in one product family does not establish a comparable implementation in every related part.
Automotive chip vendors must coordinate design qualification, authenticated diagnostics and software release methods with equipment makers. Consumer electronics companies value security features that can be maintained without disrupting applications; industrial suppliers place particular weight on long support cycles and robust recovery behavior. Developers prefer documentation that names exact processor revisions and security domains rather than high-level assurances that a hardware family is secure by default.
Historical company references also need ownership context. Cypress Semiconductor is now part of Infineon and should not be counted as a separate current public supplier. Other established processor businesses, including Qualcomm, Broadcom and Marvell, may participate in security features through complex system products; their entire corporate sales are not equivalent to device-level security revenue. Performance claims should be tied to specific supported software frameworks and verified manufacturer documentation.
Tier structure
| Tier | Companies | Basis of competition |
|---|---|---|
| Foundational silicon | NXP Semiconductors; Infineon Technologies; STMicroelectronics; Renesas Electronics | Embedded processor protection, secure boot implementations and software development resources. |
| Ecosystem platforms | Microchip Technology; Texas Instruments; Qualcomm; Samsung Electronics | Controller toolchains, protected update capabilities and highly integrated electronics. |
| System processors | Broadcom; Analog Devices; Marvell Technology Group | Specialized communications and industrial platforms with embedded trust functions. |
Key companies profiled
- NXP Semiconductors
- Infineon Technologies
- Renesas Electronics
- Microchip Technology
- STMicroelectronics
- Texas Instruments
- Qualcomm
- Samsung Electronics
- Broadcom
- Analog Devices
- Marvell Technology Group
Embedded Security Production Capacity Analysis
Embedded security capacity is not represented by one universal manufacturing line. Delivery combines processor fabrication, security intellectual property, version-controlled code, validated software libraries and OEM provisioning. Some value arises from silicon features, while other value is associated with licenses, secure update tools and service elements that belong to a protected embedded platform offering. Production readiness requires the hardware and the software release workflow to operate together.
Manufacturers can qualify a secure controller only after selecting its memory protections, debugging privileges and first-stage boot behavior. Development tools then transform signed firmware into loadable images, and factory systems enforce the activation state of each product. Errors can arise even when the cryptographic hardware is sound: a wrong image version, omitted certificate or inappropriate rollback policy may prevent a finished device from functioning safely. Clear recovery arrangements become part of production engineering rather than an optional after-sales process. Formal manufacturer and assurance references help describe the engineering task. NISTIR 8259 was updated as IR 8259 Revision 1 in April 2026, while NISTIR 8259A was published in 2020 and NISTIR 8259B in 2021. NIST SP 800-193 describes platform firmware resilience, and NIST SP 800-213 addresses connected-device cybersecurity integration for federal use. Engineers may also encounter NIST SP 800-53 Revision 5 controls, FIPS 140-2 cryptographic module context, ISO/SAE 21434 vehicle cybersecurity and IEC 62443 industrial network protections. These documents govern different concerns: an IR 8259A device capability baseline is not the same as a SP 800-193 recovery design, and an ISO/SAE 21434 vehicle program must consider more than one chip. Example processor boot systems require verification of a software image through 1 protected starting point, sometimes followed by 2 additional privileged layers. A protected runtime may isolate 2 domains, while an update program has to identify 3 states: pending installation, active image and known recovery image. Those engineering states are conceptual examples rather than mandatory industry-wide product specifications.
A trusted execution environment also needs an ecosystem of maintained libraries and tested interfaces for nonsecure application code. ST identifies Secure Manager development kits, secure module interfaces and the STM32Cube programming family among the supporting materials for selected devices. Manufacturer customers may rely on these tools through many successive firmware releases. The cost of maintaining compatibility, test procedures and security advisories can therefore outlast the original semiconductor purchase. A useful comparison is the discrete secure element that a protected microcontroller may communicate with. The NXP SE050E and SE050F differ in certification and options: Common Criteria EAL6+ is documented, and selected SE050F configurations report FIPS 140-2 module assurance levels 3 and 4 for distinct security boundaries. Its permitted crypto choices include RSA with keys up to 4096 bits, ECC to 521 bits, AES with 128-bit, 192-bit and 256-bit keys, plus SHA-1, SHA-224, SHA-256, SHA-384 and SHA-512 hashing. The package measures 3 by 3 by 0.33 mm and offers up to 50 kB protected flash, with an I2C high-speed limit of 3.4 Mbit/s and controller operation at 400 kbit/s. The specified operating range extends from −40°C to +105°C. For a different role, Microchip ATECC608C supports protected storage of up to 16 items, a 72-bit unique identifier, elliptic-curve P-256 operations and a hardware AES-128 option. Microchip also lists TLS 1.2 and TLS 1.3 key derivation, supply limits from 2.0 to 5.5 V, I/O operation from 1.8 to 5.5 V and a 1 MHz I2C option. Its published package examples include 8-pad, 8-lead and 3-lead versions. Such details are relevant to hardware/software architecture decisions, although no single component provides every runtime or update protection required by a complete electronic system.
Hardware assembly and software maintenance require different measures of readiness. An electronics supplier may have adequate packaged controllers in inventory but insufficient engineering resources to migrate a security framework after a vulnerability, or the reverse. Buyers should evaluate both component continuity and the documented ability to patch deployed products, particularly where physical systems make field replacement costly or unsafe.
Embedded Security Market Dynamics: Drivers, Restraints and Opportunities
The market grows as connected equipment introduces additional attack surfaces and product owners plan controlled software lifecycles. Security requirements are becoming more explicit in industrial, automotive and public infrastructure procurement. The opportunity is moderated by toolchain complexity, specialist workforce needs and cost constraints on low-power hardware. The impact assessment describes the combined role of these forces during the forecast period.
MARKET DRIVERS
Drivers Impact Analysis*
| Market Drivers | Impact Rank | CAGR Contribution (%) | 2026–2028 | 2029–2031 | 2032–2034 |
|---|---|---|---|---|---|
| Proliferation of networked embedded controllers | High | +3.05% | High | High | High |
| Automotive secure software architecture and update needs | High | +2.20% | High | High | Medium |
| Industrial cybersecurity and asset integrity programs | Medium-High | +1.80% | High | High | High |
| Firmware recovery and lifecycle vulnerability obligations | Medium | +1.35% | Medium | High | High |
| Availability of integrated trusted execution frameworks | Low-Medium | +0.95% | Medium | High | High |
| Others (connected care and consumer protection) | Low | +0.65% | Medium | Medium | High |
Connectivity expands software attack surfaces
Controllers installed in factories, devices and vehicles increasingly communicate outside their original physical boundaries. Remote access and shared software libraries can provide operational benefits but also introduce opportunities for unauthorized modification. A chain of trust and protected runtime can constrain some of these risks, leading product companies to treat security as a core architectural requirement rather than a feature added after a release.
Vehicle software needs authenticated transitions
Connected vehicles depend on numerous embedded components supplied by different companies. A secure update strategy must identify approved images, maintain integrity during installation and preserve usable recovery states if an update is interrupted. Greater software complexity makes those capabilities valuable during vehicle production and servicing. An OEM also needs processes for communicating security responsibilities through its component supply contracts.
Industrial operators favor verified device behavior
In automation and energy systems, a compromised control device can affect equipment uptime and potentially physical processes. Asset owners therefore ask vendors about firmware integrity, protected diagnostic access and security support periods. NIST and industry guidance offer ways of defining security capabilities, but individual plants must still test the operational consequences of the chosen controls.
Maintained security tools lower implementation effort
Integrated security frameworks help developers create partitioned code and secure firmware delivery paths without implementing every cryptographic primitive themselves. ST describes prepared services and developer workflows for suitable STM32 device families. When suppliers offer stable interfaces and traceable revisions, smaller equipment makers may find robust embedded protection more approachable within existing development schedules.
MARKET RESTRAINTS
Restraints Impact Analysis*
| Market Restraints | Impact Rank | CAGR Contribution (%) | 2026–2028 | 2029–2031 | 2032–2034 |
|---|---|---|---|---|---|
| Complexity of trusted boot and application integration | High | -1.25% | High | Medium | Low |
| Limited specialized embedded cybersecurity staffing | Medium | -0.75% | High | High | Medium |
| Legacy device software and hardware constraints | Low-Medium | -0.50% | High | Medium | Medium |
| Others (certification and lifecycle support expense) | Low | -0.10% | Medium | Medium | Low |
Architecture errors can undermine secure features
A protected processor does not automatically make a device safe. Designers must configure isolation correctly, prevent unauthorized debug access and handle keys securely across manufacturing and maintenance. Complex interaction between privileged and ordinary firmware can introduce defects. These risks increase verification work and may delay release when a product team lacks specialists experienced in embedded threat assessment.
Expertise is uneven across engineering teams
Application developers may know a controller well without being familiar with secure startup, cryptographic provisioning or authenticated recovery. Hiring and training requirements rise when product lines must support multiple processor generations. External integration partners can reduce the burden, but clear ownership of signing keys and vulnerability response cannot be delegated away without careful contracts.
Installed systems have constrained resources
A long-lived device may lack enough flash space, memory or power budget to support a modern security framework without redesign. An update that works on a recent microcontroller can exceed storage or performance limits on an earlier revision. Replacing hardware may be expensive when machinery has already passed operational and environmental qualifications, slowing deployment of new protective mechanisms.
Lifecycle assurance creates continuing costs
Security support requires monitoring new vulnerabilities, testing signed updates and retaining the ability to revoke obsolete software. Product manufacturers may need to maintain a build environment long after the original development team has moved to another design. These obligations can be particularly demanding for low-volume equipment whose commercial sales have ended while devices remain in service.
MARKET OPPORTUNITIES
Security-enabled controller ecosystems grow in value
Microcontroller vendors able to bundle tested security services, working demonstration code and stable interfaces can help customers avoid inconsistent protection practices. The commercial advantage is especially clear for embedded developers without a large in-house cybersecurity department. Device vendors still need to adapt the examples to real threat models and confirm which product configurations are supported.
Authenticated recovery can serve long-life equipment
A secure boot chain becomes more useful when equipment can recover safely from damaged or malicious code. Providers can differentiate through rollback controls, redundant images and documented support for offline maintenance. The opportunity is significant for remote industrial and infrastructure devices where a failed manual repair visit has a high operational cost.
Trusted execution supports connected medical systems
Medical device manufacturers may need to protect software that controls sensitive functionality while allowing approved updates and service access. Strong isolation can reduce the impact of a fault in less trusted application code. Successful adoption depends on safety analysis and tested clinical recovery behavior, offering room for suppliers that combine security tooling with long-term technical support.
Supply-chain attestation gains relevance
A device that can report protected boot measurements may assist fleet operators in checking the state of equipment received from multiple manufacturing partners. Such evidence can be useful during initial commissioning, software updates and incident investigation. Providers must explain the limitations of their measurements because attestation values cannot alone prove the absence of every runtime compromise.
Embedded Security Supply Chain Analysis
The commercial chain runs from security-aware processor design through firmware frameworks, factory signing systems, OEM integration and ongoing device management. Each participant handles different obligations: silicon manufacturers create protected primitives, software vendors maintain services and equipment owners decide update and recovery policy. Supply reliability involves both tangible components and continuity of supported security code.
Security architecture. Chip designers determine which hardware boundaries can isolate keys, memory and boot code. Software authors must build compatible trust services and define how ordinary applications request authorized operations. The intersection of the two disciplines shapes implementation risk and whether a product can be updated without weakening the device protection model.
Firmware production. Equipment factories generate or receive approved software images and associate them with product configurations. Signing infrastructure should restrict who can release code and maintain records of distributed versions. An apparently minor change to a build tool or certificate policy can have a significant effect on a device that verifies every image before it runs.
Integrator validation. Systems integrators test security mechanisms alongside application functionality, power loss scenarios and maintenance procedures. In a vehicle or industrial controller, an update can affect more than the local operating system. Acceptance testing should therefore include recovery actions and version-transition controls, especially when hardware from more than one supplier must communicate securely.
Installed fleet support. Once products are deployed, operators must identify affected software, schedule safe patches and retain access to trusted recovery routes. A good security supply relationship includes documentation and vulnerability notification as well as hardware availability. Customers can reduce lifecycle disruption by selecting platforms with versioned libraries and a known escalation channel.
Recent Developments in the Embedded Security Market
- April 2026 DEVICE MANUFACTURER GUIDANCE
NIST finalized revision 1 of IR 8259 foundational activities for IoT product manufacturers in April 2026. The document emphasizes security capabilities and supporting information customers need from connected equipment. This development provides context for protected software lifecycles, but it is not a measure of semiconductor market revenue. Source - 2026 STM32 SECURE BOOT DESIGN
ST technical documentation explains how secure startup differs across STM32H5 variants, separating immutable vendor-provided boot logic from optional OEM stages and later application code. Engineers can use the architecture guidance to decide whether a particular device has the isolation and cryptographic support required by a product design. Source - 2026 TRUSTED RUNTIME SERVICES
ST describes Secure Manager functions for selected STM32H5 microcontrollers, including cryptographic interfaces, internal trusted storage, initial attestation and controlled firmware updating. The framework supports integration of protected and ordinary application software while targeting specific PSA and SESIP assurance levels. Developers must still verify that the selected controller variant includes the protected resources required by their application. Source - August 2026 TRUST HARDWARE MAINTENANCE
Infineon published updated TPM security information covering hardware-rooted trust components and available firmware responses. The advisory illustrates the relationship between device-level hardware protection and the ongoing software process required to maintain customer equipment. Customers should verify component and firmware revisions when evaluating exposure. A maintenance plan should identify which signing authorities may approve security updates and how rollback is controlled. Source - September 2026 EU CYBER THREAT CONTEXT
ENISA issued a 2026 threat assessment discussing trends affecting digital systems and service operators. The material informs how businesses prioritize connected-device protection but does not represent a tally of embedded security product spending. Equipment manufacturers still need to apply their own risk assessment to select appropriate safeguards. Source - 2026 SECURE BOOT SOFTWARE
ST continues documenting its X-CUBE-SBSFU framework for verified startup and secure firmware update flows in supported device environments. Reference applications help developers understand signing, image integrity and controlled boot decisions, although each application requires validation for its exact processor and software build. Reference software is not automatically an approved field recovery system until an OEM tests it under realistic failure conditions. Source
REPORT SCOPE & SEGMENTATION
| Attribute | Details |
|---|---|
| Study Period | 2020–2034 |
| Base Year | 2025 |
| Estimated Year | 2026 |
| Forecast Year | 2034 |
| Base Market Value | USD 8,200 million |
| Forecast Market Value | USD 15,600 million |
| Forecast CAGR | 7.4% |
| Revenue Coverage | Protected embedded silicon, runtime security software and integrated security platform offerings |
| Largest Region | Asia-Pacific (~37%) |
| Currency | USD million |
| Geographic Scope | Global |
| By Type | Hardware-Rooted Security; Software-Based Security; Hybrid Solutions |
| By Application | Automotive; Industrial IoT; Consumer Electronics; Medical Devices; Others |
| By End User | OEMs; System Integrators; Device Manufacturers |
| By Security Function | Secure Boot; Runtime Attestation; Over-the-Air (OTA) Update Protection; Key Management |
| By Industry Vertical | Automotive & Transportation; Healthcare & Medical; Energy & Utilities; Smart Home & Consumer |
| By Region | Five global regional markets assessed through three representative countries and examples of connected product security adoption. North AmericaUnited States, Canada, Mexico EuropeGermany, France, United Kingdom Asia-PacificChina, Japan, South Korea South AmericaBrazil, Argentina, Colombia Middle East & AfricaSaudi Arabia, United Arab Emirates, Kenya |
| Key Companies Profiled | NXP Semiconductors; Infineon Technologies; Renesas Electronics; Microchip Technology; STMicroelectronics; Texas Instruments; Qualcomm; Samsung Electronics; Broadcom; Analog Devices; Marvell Technology Group |
| Customization Scope | Further requirements can focus on secure boot variants, processor firmware isolation, software lifecycle controls, embedded fleet management and national connected-product regulatory obligations. |
Frequently Asked Questions
How large is the embedded security market?
The global category is valued at USD 8,200 million in 2025 and forecast to achieve USD 15,600 million by 2034. These anchors imply a 7.4% CAGR for the planning interval, based on integrated hardware and software safeguards used inside connected electronic products. The boundary covers trusted execution and software updates rather than equating all cybersecurity subscriptions with electronic systems protection.
What technology has the largest type share?
Hardware-rooted security leads with an estimated ~56% because protected execution and secure startup often depend on processor features or isolated trust components. Software-based protection also matters, especially for authenticated updating and policy management, while hybrid systems combine the two approaches. The preferred design depends on physical isolation requirements, supported boot mechanisms and the ongoing firmware servicing model.
Which application produces the highest demand?
Industrial IoT represents an estimated ~29% of application value, supported by factory automation, distributed sensors and infrastructure monitoring. Compromised firmware can affect the integrity of control operations, increasing the importance of authenticated code and predictable recovery procedures across installed equipment. Buyers typically compare the software update environment and the available recovery tools before choosing an industrial controller platform.
How does secure boot operate?
A protected starting point establishes trust in the code loaded next, often by verifying a signature or measurement before allowing execution. Later stages can extend that trust to an operating system and application software. The process requires careful key handling and configuration of hardware protections. A manufacturer should also test what happens if image validation fails or power is lost while the boot chain is being changed.
What is the difference between attestation and key management?
Attestation produces evidence about a device state or selected software measurements for an external verifier, while key management governs generation, use, replacement and protection of cryptographic secrets. A mature embedded architecture can employ both, but their operational security objectives are not the same. Secure configuration monitoring can complement attestation but cannot substitute for appropriate control of signing keys.
Why is Asia-Pacific the largest regional market?
Asia-Pacific accounts for an estimated ~37% of value because connected electronics production and embedded controller design operate at scale across multiple national ecosystems. Manufacturing location alone does not establish the final destination or procurement responsibility for security software, and large engineering centers also exist elsewhere. A regional demand estimate therefore captures multiple roles, from original design through assembly to deployed device maintenance.
Who are significant embedded security vendors?
NXP, Infineon, STMicroelectronics, Microchip, Renesas and other computing semiconductor suppliers provide relevant security-capable platforms and ecosystems. Some value is delivered through firmware libraries and integration tools rather than separate packages. Cypress is part of Infineon and should not be treated as an independent current corporate rival. Platform selection should reflect the supported part number, availability of developer tools and responsibility for vulnerability disclosures.
Why are protected over-the-air updates important?
An authenticated software delivery process can reject unauthorized firmware and help equipment owners respond when previously trusted code becomes vulnerable. Designers also need safe rollback rules and resistance to interruptions, particularly when physical maintenance of a connected device would be expensive or dangerous. Maintaining version records for each unit improves response when a security advisory affects only a subset of deployed models.
What limits adoption of embedded security?
Specialist engineering effort, legacy processor constraints and long-term software support obligations can raise total implementation cost. A strong hardware feature may be difficult to use safely without the appropriate application architecture, testing expertise and trusted production workflow. These barriers can postpone upgrades in long-lived equipment. A supplier providing validated libraries and responsive technical support can reduce, but not eliminate, this cost.
Are embedded security and secure components identical markets?
No. The broader embedded security category covers protected firmware, trusted execution, boot integrity and managed software updating alongside security-capable silicon. A narrowly defined hardware security product category concentrates on individual secure devices and their associated capabilities. Separate market forecasts should be evaluated on their own terms. Their different system boundaries make a direct addition or subtraction of the two titles inappropriate.
Research Sources & Evidence Base
Get Sample Report PDF for Exclusive Insights
Report Sample Includes
- Table of Contents
- List of Tables & Figures
- Charts, Research Methodology, and more...
 Download Sample Report PDF